Gamaredon's Evolving Tactics in Cyberespionage: A 2025 Analysis
ESET Research's latest report examines the tactics and tools employed by Gamaredon, a prominent Russia-aligned cyberespionage group, throughout 2025. The analysis highlights the group's increased reliance on legitimate online services to obscure its operations and the introduction of new tools aimed at enhancing its capabilities against Ukrainian targets amid ongoing geopolitical tensions.
ESET Research has provided an in-depth analysis of Gamaredon, one of the most active Russia-aligned advanced persistent threat (APT) groups, which has been targeting Ukraine amidst the ongoing conflict. The group's operations in 2025 have shown a significant evolution in tactics, particularly in how it conceals its command and control (C&C) infrastructure and exfiltrates stolen data. The report details Gamaredon's increased reliance on legitimate online services to mask its operations, making it a formidable threat in the cyber domain.
Throughout 2025, Gamaredon maintained a high operational tempo, focusing primarily on Ukrainian governmental and military institutions. This focus aligns with Russia's geopolitical objectives, aiming to gain an intelligence advantage through the exfiltration of sensitive information. The group's activities were attributed to the 18th Center of Information Security of Russia's FSB, underscoring its state-sponsored nature.
The Dead Drop Gift Shop
Sponsorship mission accomplished.
One notable aspect of Gamaredon's strategy was its collaboration with other Russia-aligned threat actors, such as Turla. This partnership highlights the potential for coordinated cyberespionage efforts among these groups, amplifying their operational impact. The report also notes that Gamaredon's activities were closely monitored, with significant shifts in their tactics observed throughout the year.
In the first half of 2025, Gamaredon introduced six new tools, primarily focused on enhancing delivery methods for its malware. These tools were developed before major holidays in Russia and Crimea, suggesting a strategic approach to timing and operational planning. The report indicates that the group also employed new techniques, such as abusing a vulnerability in WinRAR to establish persistence in compromised systems.
Gamaredon's spearphishing campaigns became larger and more frequent in the latter half of the year, with a notable increase in the use of HTML smuggling techniques to deliver malicious payloads. The report documented 35 spearphishing campaigns throughout the year, revealing a marked uptick in activity and sophistication. Additionally, the group utilized custom weaponizers for lateral movement within networks, further complicating detection and response efforts.
Innovative Espionage Techniques Unveiled
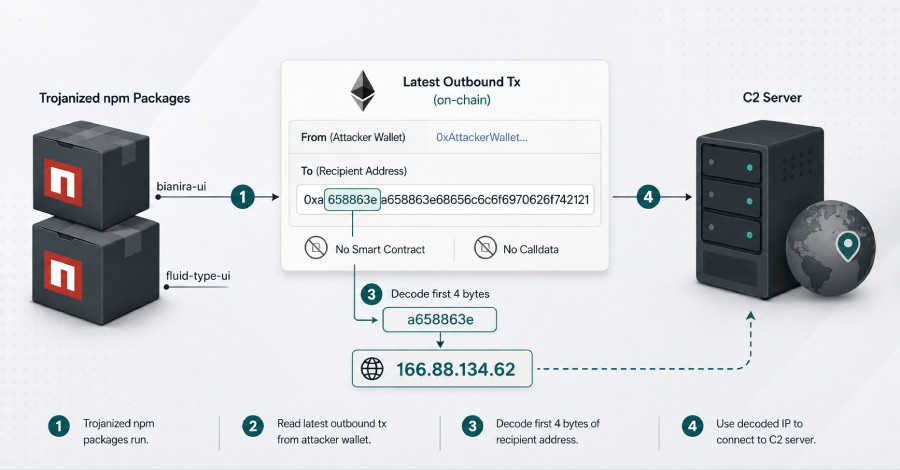
A significant development in Gamaredon's operations was its heavy use of dead-drop services, a concept borrowed from traditional espionage. This method allowed the group to retrieve critical information from legitimate websites, complicating efforts to block their activities. By embedding malicious instructions within legitimate platforms, Gamaredon was able to maintain operational flexibility and evade detection.
The report also highlights Gamaredon's evolving infrastructure for data exfiltration, as the group upgraded its file-stealing tools to utilize cloud storage services. This shift not only reduced the need for maintaining its own infrastructure but also helped blend malicious traffic with legitimate service usage. As the year progressed, Gamaredon increasingly relied on third-party services to obscure both its operational commands and the destination of stolen data.
As 2025 concluded, ESET Research noted that Gamaredon continued to pose a significant cyberespionage threat to Ukrainian institutions, with no indications of a shift in focus. The group's operational methods, characterized by simplicity and persistence, combined with a creative use of legitimate online services, suggest that Gamaredon will remain a prominent player in the cyberespionage landscape as long as the conflict persists.
New Tools and Techniques Introduced
The introduction of six new tools in 2025 marked a notable expansion of Gamaredon's capabilities. These tools, primarily written in PowerShell, were designed to enhance the group's delivery methods and improve the effectiveness of its cyber operations. Among these tools, PteroPaste stood out due to its complexity, combining various functionalities to facilitate the execution of malicious payloads. The evolution of these tools reflects Gamaredon's strategic focus on maintaining an adaptable and effective cyber arsenal.
As the conflict in Ukraine continues, the insights provided by ESET Research serve as a critical reminder of the evolving nature of cyber threats and the importance of vigilance in cybersecurity measures. The ongoing developments in Gamaredon's operations underscore the need for robust defenses against increasingly sophisticated cyberespionage tactics.