New Malware Technique Hides C2 IP in Ethereum Transfers
Cybersecurity researchers have identified a new malware technique that conceals command-and-control (C2) server IP addresses within Ethereum transaction recipient addresses. This method, dubbed NullReceiver, represents an evolution of the EtherHiding technique and has been linked to North Korean hacking groups. The discovery highlights the ongoing sophistication of cyber threats and their implications for digital security.
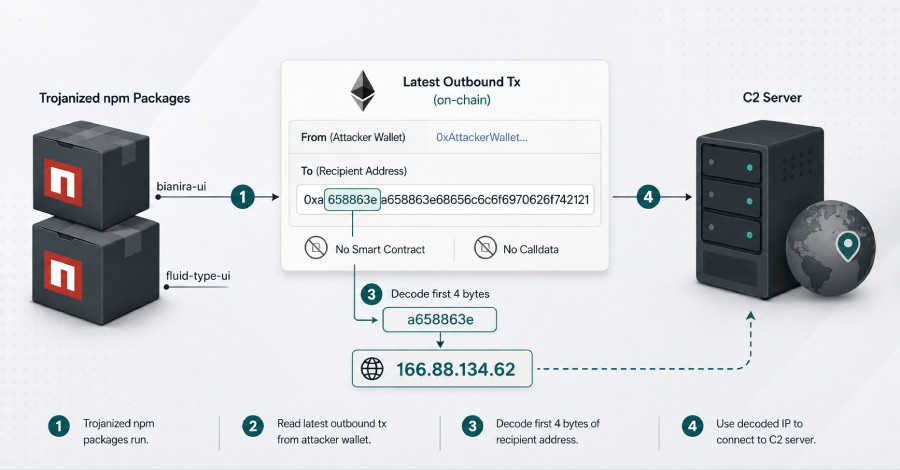
Cybersecurity researchers have flagged a significant evolution in malware tactics with the introduction of a technique known as NullReceiver. This method conceals command-and-control (C2) server IP addresses within the recipient addresses of empty Ethereum transactions, marking a notable advancement from the previously documented EtherHiding technique. The discovery of this new dead drop resolver approach was made in relation to two trojanized npm packages, "bianira-ui" and "fluid-type-ui," which have been linked to North Korean cyber actors.
The packages in question have been removed from the npm repository, but they garnered a few hundred downloads since their publication on July 28, 2026. The EtherHiding technique, first reported by Guardio Labs in October 2023, involved embedding malicious code within smart contracts on public blockchains such as Ethereum or BNB Smart Chain. This method was praised for its ability to provide enhanced operational resilience against takedown efforts.
The Dead Drop Gift Shop
Sponsorship mission accomplished.
The North Korean hacking groups' use of EtherHiding was outlined by the Google Threat Intelligence Group (GTIG) in connection with a long-running campaign called Contagious Interview. This campaign sought to deceive targets via LinkedIn, offering lucrative job opportunities that ultimately led to malware deployment. The emergence of the NullReceiver technique suggests that these threat actors are refining their tactics to evade detection further.
According to security researcher Paul McCarty, NullReceiver encodes the C2 IP address directly in the bytes of a recipient address for a zero-value Ethereum transfer, circumventing the need for a smart contract or payload field. This innovation addresses a key limitation of EtherHiding, which required a fixed destination address that could be monitored by defenders. By using a non-existent destination address, the NullReceiver method complicates attribution efforts and enhances the stealth of the operation.
Advancements in Stealthy Malware Techniques
The new technique has been described as more discreet than its predecessor. Each transaction utilizes a unique, throwaway address, making it difficult for defenders to track. Unlike EtherHiding, which allowed for the smuggling of full URLs or scripts, NullReceiver is limited to encoding only a few bytes of information. OpenSourceMalware, which identified the NullReceiver technique, noted that the absence of a fixed target and fingerprint, combined with lower transaction costs, makes this method particularly insidious.
As of now, 68 transactions have been recorded since the packages were published. Each transaction's destination address is consistent, with the hexadecimal string "0xa658863ea658863e68656c6c6f6970626f742121" encoding the C2 IP address and an ASCII string. This encoding method allows the threat actors to extract the IP address without leaving a traceable footprint.
The Debrief
OpenSourceMalware has also identified an additional five packages utilizing the NullReceiver technique, indicating a broader campaign linked to North Korean threat actors. Jenn Gile, co-founder of OpenSourceMalware, highlighted the reuse of cryptocurrency wallets by these actors, which has facilitated connections between the newly discovered npm packages and existing campaigns. The shared infrastructure has led to the identification of over 20 other compromised packages across various ecosystems, all linked to a campaign known as PolinRider. This campaign has reportedly spent months infiltrating developer machines through various deceptive tactics, including fake interviews and malicious code.
The implications of these developments are significant, as they underscore the evolving landscape of cyber threats and the need for heightened vigilance in digital security practices.